Skip to content

Intune

Ignite 2026 for Intune, Entra and Windows 365 admins: what's GA and what's preview
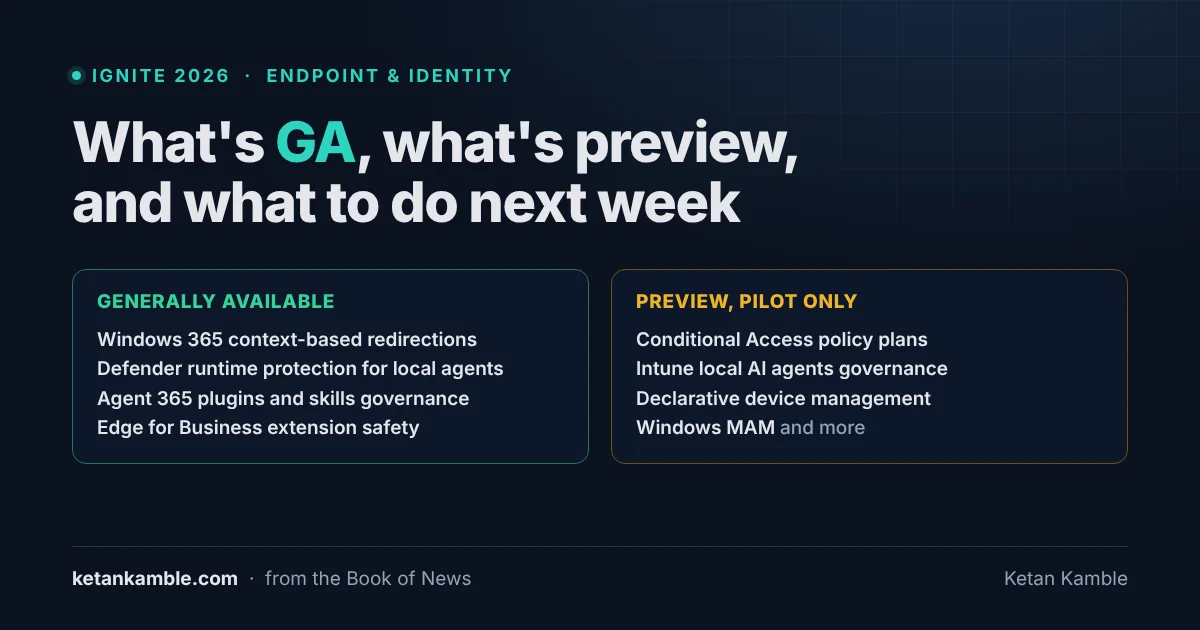
Ignite 2026 for endpoint and identity admins. Generally available: Windows 365 context-based redirections, Defender runtime protection for local agents, Agent 365 plugins and skills governance, Edge for Business extension safety. Preview, pilot only: Conditional Access policy plans, Intune local AI agents governance, declarative device management, Windows MAM

Short answer, four Ignite 2026 items for endpoint and identity admins are generally available now: Windows 365 context-based redirections, Defender runtime protection for local AI agents (with caveats I cover below), Agent 365 plugins and skills governance and Edge for Business extension safety, and they're the ones I'd look at first. The headline Intune and Entra items, like Conditional Access policy plans and local AI agents governance, are still preview. Status here is as of 20 November 2026.

Ignite ran 17 to 20 November in San Francisco and online, and there's a lot in the Book of News this year. I went through it for one thing, which of these can go to change next week and which are still preview, fine for a pilot but not something I'd put in production yet.
When Apple jumps a version, your Intune compliance quietly drifts

Cover: Apple ships a new major iOS version, a public feed catches it overnight, and an email lands the next morning telling you to raise the Intune OS-version compliance floor

We keep our Apple devices on an n-1 compliance line. Corporate devices have to be on the latest major iOS or one version behind it, personal devices one more back than that, and the same idea on macOS for the corporate ones. For years that was simple math. iOS 18 is out, so the floor is 17, and a quick check every September kept us honest.

Then Apple changed how it numbers things. iOS 18 didn't become iOS 19, it jumped straight to iOS 26. Any rule that worked out the floor by subtracting one from the current number was suddenly wrong, and a compliance policy can drift like that for weeks before anyone notices, usually when a device that should have been blocked quietly is not. This is the small automation we built so we stop finding out late.

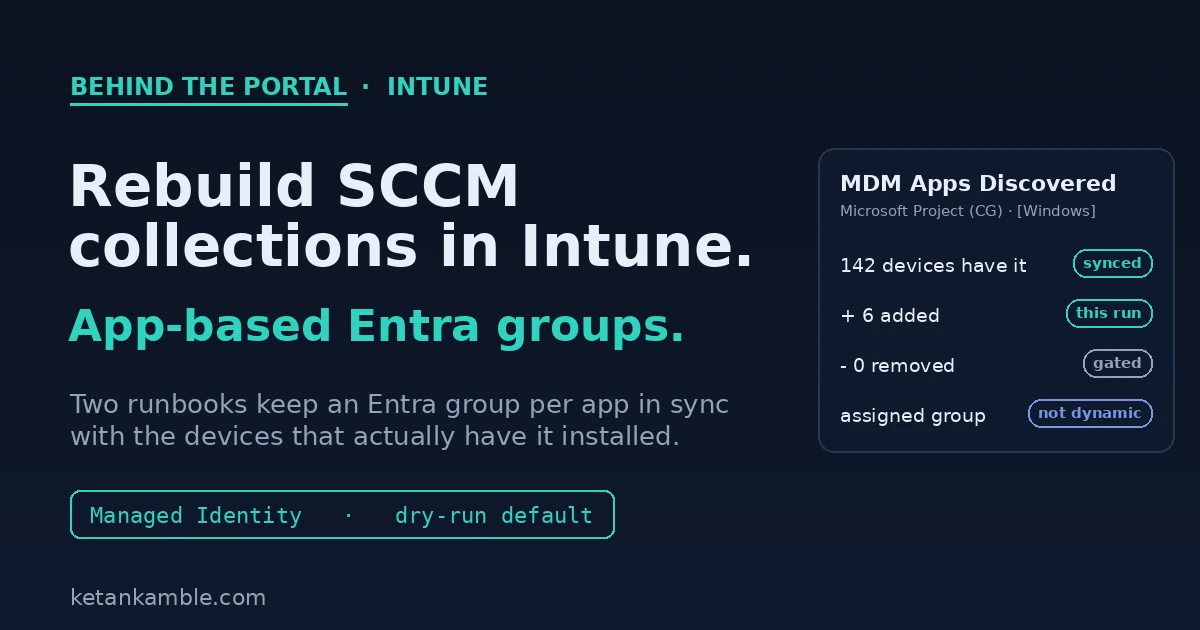
App-based Entra groups to replace SCCM collections

Cover: two Azure Automation runbooks reading Intune detected-apps inventory and keeping an Entra group per app in sync with the devices that have it installed

We have been winding down Microsoft Configuration Manager, what most of us still call SCCM, like everyone else. The thing I miss most is not the console, it's collections. A collection that says "every device that has this app installed" was how we targeted an update, and Intune has nothing like it.

Ugur Koc already wrote a script that rebuilds that idea from Intune's own inventory, and it's where I started. On a normal tenant it works well. On our 17,500-device estate it didn't, so I re-engineered it for scale and for running unattended, and that re-engineering is what this post is really about.

This one is also different from most of what I write here. It writes. It changes Entra group membership, so I can't dress it up as read-only. What I did instead was make the writing part paranoid, and that turned out to be the interesting bit.

Audit your new Intune Suite features, read-only first

Cover: advanced Intune Suite features arriving switched on at the license level, and a read-only Graph audit listing which are present before anyone enables them

Around the start of July, a few of our Microsoft 365 E5 tenants quietly grew some new powers. Nobody deployed anything. Microsoft just included a batch of advanced Intune Suite capabilities as part of the license, and there they were. My first reaction was not "great, let's turn them on". It was "hang on, what exactly is available now, and who can already touch it?"

That question, what is on before I start changing things, is the whole point of this post. Before you configure a single new policy, it is worth taking a read-only look at what the license just handed you.

Governing Intune device wipes with Multi Admin Approval

Cover: an Intune device-wipe request stopped at a two-person approval gate, with a read-only runbook alerting and reporting on every approval

A while back a device wipe request sat in our Intune approval queue for most of a day before anyone noticed it. Nothing was broken. That is just how Multi Admin Approval works, and it is the gap this post is about.

If you have turned MAA on for device wipe and retire, you already know the good part. One admin asks for the wipe, a different admin has to approve it, and no single person can factory reset a laptop on their own. I like it. It is the kind of guardrail that should have been in the product years ago.

Here is the part nobody warns you about. Microsoft gave you the gate, but it forgot the doorbell. There is no email when a request comes in, no ticket, nothing shows up on a dashboard. It quietly assumes someone is sitting in Tenant administration > Multi Admin Approval > Received requests all day, and in real life nobody does that. So legitimate wipes stall, the service desk opens "wipe not working" tickets that were never broken, and months later nobody can tell you who approved what.

I did not want to give my one admin a new job of babysitting that screen. So I built the missing half instead. It is a small read-only runbook that watches the queue, emails the service desk the moment a request lands, and keeps its own history for Power BI. It can read the approval requests and nothing else. It cannot approve, it cannot reject, it cannot wipe. Below is how it works and how to set it up in your own tenant.

MAA now intercepts Graph API calls — and why read-only never sees it

Cover: Multi Admin Approval intercepts a Graph write with 412 Precondition Failed, while the read sails through 200 OK

My automation started failing on a write with a status code I did not expect: 412 Precondition Failed. Not 403 Authorization_RequestDenied — I know that one, that's a missing scope. A 412, on a POST to Intune, telling me a precondition hadn't been met. The precondition, it turned out, was a second admin's approval. What had changed was Multi Admin Approval (MAA) — previously an interactive-admin-only gate — extended to app-authenticated Graph calls. If your tenant has an MAA access policy on a protected workload, your service principal now hits the same wall a human admin does.